

COMPREHENSIVE AI COMPLIANCE SOLUTIONS
Four Integrated Services for
Digital Trust & Regulatory Compliance
Choose individual services or combine them for comprehensive AI compliance, governance, testing, and security. Each service is designed to address specific regulatory and organizational challenges while working seamlessly together.
Why Choose Integrated Services
Services That Work Together to Build Digital Trust
Our integrated approach ensures your compliance, governance, testing, and security efforts align and reinforce each other
How Our Services Work Together
Compliance requirements inform governance policies. Governance frameworks guide testing standards. Secure foundations enable rigorous validation. This integrated approach eliminates silos and ensures your entire organization moves toward digital trust together.

Compliance meets all regulatory demands; goverance drives the internal discipline to sustain them.

Testing
Governance sets standards for consistency; testing provides empirical proof of adherence.

Data Security:
Testing validates product safety and quality; data security safeguards the integrity of all associated information.

Compliance:
Data security protects sensitive information; compliance ensures that protection meets all regulatory requirements.
Customized Solutions for Your Organization
Whether you're a startup needing immediate product compliance or an enterprise establishing organization-wide AI governance, we design solutions that fit your specific needs, budget, and timeline.
During our discovery phase, we assess your current compliance maturity, understand your regulatory obligations, identify your biggest risks, and design a phased engagement that delivers quick wins while building toward comprehensive digital trust.
OUR IMPACT
Proven Results
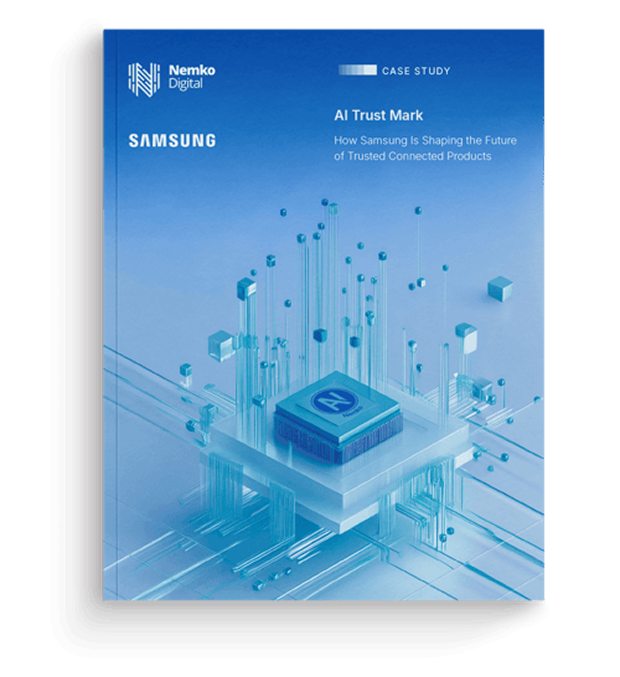
AI Trust Mark: How Samsung Is Shaping the Future of Trusted Connected Products
Samsung Electronics, the global leading manufacturer of consumer electronics and home appliances, was developing an advanced remote support system for connected home appliances. The system enables authorized technicians to remotely diagnose, troubleshoot, and resolve issues, significantly improving service efficiency while reducing the need for on-site interventions. By analysing operational data, the system can detect potential issues early, including equipment malfunctions, abnormal usage patterns, and maintenance needs.
Latest Insights & Expert Guidance
Essential AI
Governance Resources
Accelerate your AI governance journey with practical, evidence-based insights from our global experts. Download our comprehensive whitepapers and guides to turn complexity into clarity.
A case study on how a multinational connected-product provider turned EU Data Act requirements into a practical framework for data access, ownership, contracts, technical controls, and ongoing governance.
A collaborative whitepaper outlining practical AI governance principles across the lifecycle, co-developed with Deeploy and leading AI trust companies to turn complexity into competitive advantage.
Reflect on 2025's key AI developments and explore the four themes shaping 2026: strategic AI procurement, governance tooling, AI agents, and evolving global regulation.
A practical GenAI governance and control framework that translates risk, ethics, and regulation into actionable controls, enabling safe deployment and scalable adoption.
How Samsung achieved AI Trust Mark certification for its remote support platform, establishing scalable governance, regulatory alignment, and increased trust in connected products.
A practical guide for embedding trustworthy AI into electronics and connected systems, co-developed with IBM to address regulatory readiness, agentic AI, and scalable trust frameworks.
A structured GenAI governance framework enabling a Dutch public sector organization to move from pilots to production with clear risk management, controls, and regulatory readiness. (Dutch version)
Discover how a global smart device manufacturer built a focused regulatory compliance strategy, reducing scope by 30-50% across 17+ EU frameworks.

A practical guide to identifying, assessing, and managing AI risk through proportionate controls, clear ownership, and continuous governance across the AI lifecycle.
A case study on how a global healthcare education manufacturer classified 70+ connected products, reduced unnecessary conformity burdens, and built a prioritized roadmap for EU Cyber Resilience Act readiness.
A case study on how an EV charging provider strengthened privacy governance, clarified international data processing, and created a prioritized GDPR roadmap to support European expansion.