Skip to content

CRA Implementation: What Manufacturing Leaders Need to Know

Your Complete 2027 Compliance Roadmap

The EU's Cyber Resilience Act is reshaping product cybersecurity requirements for manufacturers. CRA compliance implementation means integrating cybersecurity across product design, vulnerability management, technical documentation, and lifecycle support. By December 2027, compliance is mandatory. The question isn't whether it applies to you—it's whether you're ready.

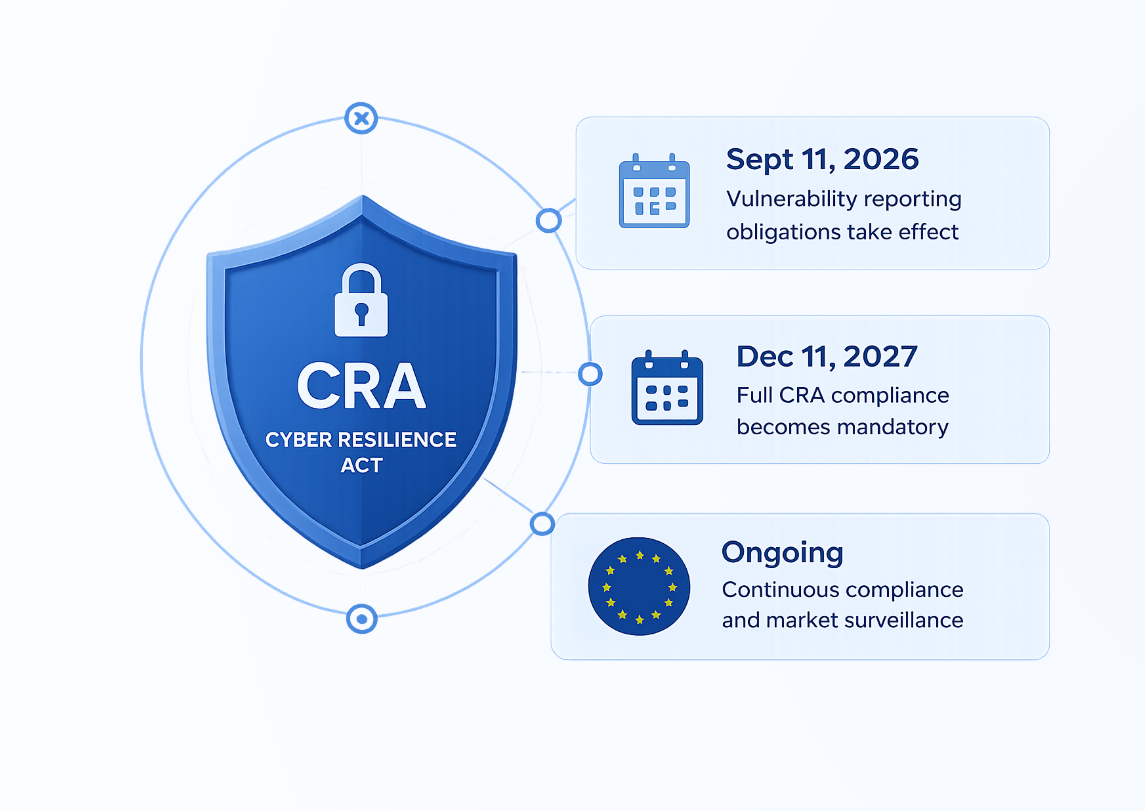
CRATimeline-Infographic

What Is CRA Implementation?

CRA implementation refers to the process of aligning your products and operations with the EU's Cyber Resilience Act. The regulation requires manufacturers to embed security into product design, manage vulnerabilities throughout the product lifecycle, and maintain comprehensive documentation.

The enforcement timeline is tight: vulnerability reporting begins September 2026, and full compliance is required by December 2027.

Why It Matters

Non-compliance carries serious consequences that extend far beyond regulatory fines. Manufacturers must understand the business impact of failing to meet CRA requirements.

Market Access

Products that don't meet CRA requirements cannot be legally sold in the European Union.

Financial Penalties

Fines can reach up to €15 million or 2.5% of your global annual turnover.

Supply Chain Risk

You are now responsible for cybersecurity across your entire supplier network and software components.

Competitive Disadvantage

Enterprise customers are already requiring CRA compliance from their suppliers in new contracts.

The Manufacturing Challenge

Manufacturing organizations face unique obstacles.

Supply chain complexity

Managing cybersecurity visibility across multiple vendors and components

Legacy infrastructure

Retrofitting security into long-lifecycle industrial equipment

Continuous vulnerability management

Monitoring and reporting vulnerabilities for years post-deployment

What Happens Next?

The path to CRA readiness depends on your specific situation. Every organization's product portfolio, supply chain, and current security maturity is different.

The first step is understanding where you stand and what your organization needs to address. That's where expert guidance makes the difference.

2026
Sep 11, 2026

Vulnerability reporting obligations begin

2027
Dec 11, 2027

Full CRA compliance becomes mandatory

CRA Checklist Cover Mockup (1)

Your Next Step Toward Compliance

Download the CRA Compliance Roadmap and get the expert guidance you need to understand requirements, assess your readiness, and build a path to compliance.

Practical guidance you can use
Expert insights from regulatory specialists
Start your compliance journey today

Need Help Implementing CRA Requirements?

Nemko Digital can help you assess your current readiness, identify compliance gaps, prioritize implementation activities, and build a practical path toward CRA compliance.

CRA Readiness Assessment

Evaluate your current infrastructure against CRA requirements and identify gaps in operational readiness.

Gap Assessment

Comprehensive analysis of your product ecosystem to determine which components fall under CRA jurisdiction.

Compliance Consulting

Strategic guidance on implementing cybersecurity measures aligned with regulatory expectations and industry best practices.

0+ Years of Trust
0+ Countries Served
0+ Clients Worldwide
Experts Regulatory